This guide covers everything you need to know about time-stamping digital content:
- What it is: A process that adds a verified date and time to digital records
- Why it matters: A verified timestamp can help show that data matching a file hash existed by a stated time; it does not identify the author or prevent later changes
- How it works: Uses cryptography and trusted time sources to create verifiable timestamps
- Key components: Time source, timestamp server, client application, digital signature
- Standards: RFC 3161, ETSI EN 319 421/422, eIDAS regulation
- Implementation: Choose a protocol, select a TSA, generate document hash, create and verify timestamp
- Security: Use strong algorithms, regular audits, multiple authentication factors
- Legal aspects: Follows e-signature laws, data protection rules, industry regulations
- Future trends: Blockchain integration, AI-powered verification, quantum-safe algorithms
Quick Comparison of Time-Stamping Methods:
| Method | Security | Cost | Ease of Use | Blockchain-Based |
|---|---|---|---|---|
| Traditional TSA | High | Medium | Medium | No |
| Blockchain | Very High | Low | Medium | Yes |
| Distributed Ledger | High | Medium | Complex | Partial |
| Quantum-Safe | Very High | High | Complex | No |
Related video from YouTube
How Time-Stamping Technology Works
Basics of Cryptographic Time-Stamping
Cryptographic time-stamping adds a verifiable date and time to electronic records. It uses digital signatures to prevent tampering. The process involves:
1. Hashing: Creating a unique digital fingerprint of the document
2. Timestamping: Combining the hash with the current time
3. Signing: Adding a digital signature to the timestamp
This creates a record showing a specific document existed at a particular time.
Parts of a Time-Stamping System
A time-stamping system has these key parts:
| Component | Function |
|---|---|
| Time Source | Provides accurate time, often synced with atomic clocks via NTP |
| Timestamp Server | Processes requests and creates timestamp responses |
| Client Application | Sends timestamp requests for documents or transactions |
| Digital Signature | Ensures the timestamp is genuine and unchanged |
Timestamp servers can be software programs or hardware devices, depending on security and speed needs.
What Time Stamping Authorities (TSAs) Do
Time Stamping Authorities (TSAs) play a key role in time-stamping:
- Act as trusted third parties to confirm when data existed
- Issue timestamp tokens that include:
- The document’s hash
- The timestamp
- The TSA’s digital signature
- Undergo regular checks to meet standards like eIDAS (Europe) and ESIGN (US)
- Sign timestamp tokens so a verifier can detect changes to the token; verification does not prevent later changes to the original data
TSAs use Hardware Security Modules (HSMs) to store their private signing keys, adding extra security to time-stamping.
Real-World Application of Time-Stamping
Time-stamping is used in various industries:
| Industry | Use Case | Example |
|---|---|---|
| Legal | Document signing | E-signatures with timestamps prove when contracts were signed |
| Finance | Transaction records | Banks use timestamps to track exact times of trades or payments |
| Healthcare | Patient records | Hospitals timestamp medical records to show when they were created or updated |
| Technology | Software development | Git uses timestamps to track code changes and version history |
Creating a Timestamp
To create a timestamp in common software:
1. In Adobe Acrobat:
- Set up the software with a timestamp server
- Create a signature field
- Choose the signing certificate generator
2. In Microsoft Word:
- Change registry entries to allow timestamps
- Make a signature line to sign the document
Verifying a Trusted Timestamp
To check a trusted timestamp:
- Get the hash of the original data
- Get the timestamp token
- Get the TSA’s certificate
- Compare the original data’s hash with the hash in the timestamp token
- Check the TSA’s signature against its certificate
Verification can confirm that the token’s signature is valid and that the current file’s hash matches the stamped hash. This makes later changes detectable; it does not establish authorship.
Standards for Secure Time-Stamping
Time-stamping must follow these standards:
- RFC 3161 and RFC 5816: Main standards for secure cryptographic timestamping
- ETSI EN 319 421 and ETSI EN 319 422: European standards for trusted time-stamping
These standards make sure timestamps are secure and can be trusted.
Long-Term Digital Signatures
Time-stamping helps with long-term digital signatures:
- Proves when a document was signed, even after the signer’s digital credentials expire
- Works with different signature formats:
- PAdES for PDF documents
- XAdES for XML
- CAdES for other data types
This is crucial for legal documents that need to be valid for many years.
Time-Stamping Rules and Guidelines
RFC 3161 Time-Stamp Protocol (TSP)
RFC 3161 sets the standard for secure cryptographic time-stamping:
- Uses Cryptographic Message Syntax (CMS) SignedData
- Includes a signed attribute to identify the signer’s certificate
- Keeps time-stamped data safe and genuine
Microsoft Authenticode Time Stamping
Microsoft Authenticode applies digital signatures to binary data, mainly software:
- Keeps signed software valid after the signing certificate expires
- Works with code signing
- Checks validity based on signing time, not current time
Other Key Standards
| Protocol | Main Features |
|---|---|
| RFC 5816 | Adds extra security to RFC 3161 |
| ETSI TS 101 861 | European standard, works with RFC 3161 |
| ISO/IEC 18014 | International time-stamping service standard |
Implementing Time-Stamping
- Pick a protocol that fits your needs and rules
- Make sure your Time Stamping Authority (TSA) follows the protocol
- Check your time-stamping process often for safety and compliance
Time-Stamping in Code Signing
Time-stamping is a key part of code signing:
- It’s optional but highly recommended
- Keeps code signing signatures valid even after the certificate expires
- Uses a Time Stamping Authority (TSA) to add a trusted time stamp
How Time-Stamping Works in Practice
- The client app connects to the TSA service
- It sends a hash of the code for time-stamping
- The TSA sends back a time stamp token
- This token is saved with the document or code signature
Benefits of Time-Stamping
- Allows software to work on operating systems even after the certificate expires
- Proves when a document was signed
- Helps with long-term digital signatures
Tips for Effective Time-Stamping
- Always use time-stamping when signing code
- Choose a trusted TSA that follows industry standards
- Keep your time-stamping process up-to-date with the latest security practices
How Time-Stamping Works Step-by-Step
Time-Stamping Process Flowchart
The time-stamping process follows these steps:
- Client creates data hash
- Client sends hash to Time Stamping Authority (TSA)
- TSA adds timestamp and signs
- TSA returns signed token to client
- Client checks token
- Client saves or attaches token
Client Actions
The client performs these tasks:
| Step | Action | Description |
|---|---|---|
| 1 | Hash Creation | Make a cryptographic hash of the content |
| 2 | Request Preparation | Set up a time-stamp request with the hash |
| 3 | TSA Contact | Send the request to a trusted TSA |
| 4 | Token Check | Make sure the received time-stamp token is valid |
| 5 | Token Storage | Keep the token safe or attach it to the content |
TSA (Server) Actions
The Time Stamping Authority does the following:
- Handle Requests: Get and check incoming time-stamp requests
- Make Timestamp: Create an exact timestamp using a trusted time source
- Build Token: Join the timestamp with the client’s hash
- Sign: Use the TSA’s private key to sign the time-stamp token
- Reply: Send the signed token back to the client
Checking Time-Stamp Authenticity
To verify a time-stamp:
- Look at Token: Check the time-stamp token structure
- Verify Signature: Use the TSA’s public key to check its digital signature
- Check Certificate: Make sure the TSA’s certificate is valid and trusted
- Time Check: Confirm the timestamp is within a reasonable range
- Compare Hash: Check that the document’s current hash matches the stamped hash
Timestamping and Ownership Resources
For related context, see DocuSign and our guide to establishing ownership with timestamps.
Cryptography in Time-Stamping
Hash Functions in Time-Stamping
Hash functions create a unique digital fingerprint of the content being time-stamped. Common hash functions used in time-stamping include:
| Hash Function | Output Size | Use Case |
|---|---|---|
| SHA-256 | 256 bits | Most common, used in Bitcoin |
| SHA-3 | Variable | Newer, more resistant to attacks |
| BLAKE2 | Variable | Fast, used in some cryptocurrencies |
Benefits of using hash functions:
- Protect content integrity
- Reduce data transmission
- Keep content private
Digital Signatures for Authenticity
Time Stamping Authorities (TSAs) use digital signatures to prove the authenticity of timestamps. This process involves:
1. TSA receives a hash of the document
2. TSA adds the current time to the hash
3. TSA signs the combined data with its private key
4. TSA sends the signed timestamp back to the client
This method ensures:
- The timestamp comes from a trusted source
- The TSA can’t deny creating the timestamp
- Any changes to the timestamp are detectable
Public Key Infrastructure (PKI) in Time-Stamping
PKI forms the backbone of trust in cryptographic time-stamping. It manages:
- TSA identity verification
- Secure key management
- Trust hierarchies
- Certificate revocation
When evaluating a timestamp provider such as DigiCert, review its current documentation for time-source controls, key management, certificate validation and service limits.
Real-World Application: Microsoft Authenticode
Microsoft Authenticode is a widely used standard for time-stamping in Windows applications. It works like this:
1. Developer signs their code 2. Code is sent to a TSA for time-stamping 3. TSA returns a signed timestamp 4. Timestamp is embedded in the code signature
This process allows signed software to remain valid even after the developer’s certificate expires.
Implementing Time-Stamping: Key Steps
To implement time-stamping in your systems:
- Choose a trusted TSA
- Generate a hash of your document (e.g., using SHA-256)
- Create a timestamp request following RFC 3161 standards
- Send the request to the TSA
- Verify the returned timestamp token
- Store or attach the timestamp to your document
"Proper implementation of cryptographic time-stamping is crucial for maintaining the long-term validity and integrity of digital signatures," says Dr. Carlisle Adams, co-author of RFC 3161.
Using Time-Stamping for Digital Content
Choosing a Time-Stamping Method
When picking a time-stamping method for digital content, think about:
- Security: Use methods that leverage blockchain-based timestamps for content security to ensure better safety and public checking.
- Cost: Compare the provider’s fees, billing basis and any volume minimums.
- Ease of use: Look for services that are easy to set up and use.
Adding Time-Stamping to Your Work
To start using time-stamping:
- Find important files that need timestamping (like legal papers, creative work, or computer code).
- Pick a good time-stamping service that fits your needs and budget.
- Set up automatic timestamping for new or changed files.
- Teach your team why time-stamping is important and how to do it right.
Tips for Good Time-Stamping
Follow these tips to get the most out of time-stamping:
- Timestamp documents before sharing them to protect your work.
- Use time-stamping for important files to show they haven’t been changed.
- A timestamp can help show when a matching file hash existed; it does not prove the file is the original or identify its creator.
- Check your timestamped files regularly to make sure they’re still valid.
- Keep good records of what you’ve timestamped and why.
| Content Type | When to Timestamp |
|---|---|
| Legal Documents | Before sending to court |
| Creative Works | Before making public |
| Dashcam Footage | Right after recording |
| Computer Code | After big changes |
Real-World Examples
Here are some ways people use time-stamping:
"I use it to check important documents before court. It’s an extra step to make sure our evidence is solid," says Jena Karlis, a paralegal.
"I always timestamp dashcam footage right away," says John Larson, an insurance expert. "Some people try to change accident videos to trick insurance companies."
Why Use Time-Stamping?
Time-stamping helps in many ways:
- A verified timestamp can support that a matching hash existed by a given time; it does not identify who created the file.
- It’s faster and cheaper than getting a copyright or trademark.
- A timestamp token binds a file hash to a time assertion; comparing hashes can reveal later changes to the file.
- A timestamp does not establish authorship; keep records that identify the creator and document custody of the file.
How Time-Stamping Works
Some services anchor hashes in a blockchain. A verifiable record may show that a matching hash was recorded by a particular time, but it does not establish authorship or prove that the file’s contents are true. What can be checked depends on the service’s method and the records it provides.
sbb-itb-738ac1e
Keeping Time-Stamping Safe
Weak Points in Time-Stamping
Time-stamping systems can have these weak spots:
- TSA Key Breach: If someone steals a Time Stamping Authority’s private key, all its timestamps become untrustworthy.
- Clock Issues: Wrong time sources can make incorrect timestamps, which can ruin the whole process.
- Hash Problems: As hash functions get better, old ones might become weak, making timestamps less secure.
Ways to Make Time-Stamps Safer
To boost time-stamp safety:
- Use Strong Math: Pick tough hash functions and encryption to protect timestamps.
- Check Often: Look at TSA systems and how they work regularly to find and fix weak spots.
- Use Multiple Checks: Make people prove who they are in more than one way to use TSA systems.
- Get Good Time Sources: Use several trusted time sources to make sure timestamps are right.
Long-Term Time-Stamp Issues
Keeping time-stamps good for a long time can be hard:
- Old Math: As math methods get old, you might need to update timestamps with newer, stronger math.
- Keeping Data Safe: Storing time-stamped data for a long time and making sure you can still use it later can be tricky as tech changes.
- Legal Stuff: Making sure time-stamps stay legally valid for a long time might mean following new rules as they come out.
To fix these problems:
- Set up a way to update timestamps with new math protection every so often.
- Make a good system to store data with backups and regular checks.
- Keep up with new laws and change how you do time-stamping to follow them.
Assessing Time-Stamping Provider Security
| Company | Action Taken | Result |
|---|---|---|
| DigiCert | Reader check: Review DigiCert’s current documentation for its time source and security controls. | This check confirms only the time-source and security controls DigiCert documents, with supporting evidence; undocumented controls remain unconfirmed. |
| Sectigo | Reader check: Check Sectigo’s current documentation for its timestamp-token validation process and certificate details. | This check confirms only the token-validation steps and certificate details in Sectigo’s current documentation; undocumented controls remain unconfirmed. |
| GlobalSign | Reader check: Review GlobalSign’s published service terms for timestamping, including stated limits and support arrangements. | This check confirms only the service terms, limits and support arrangements GlobalSign publishes; unstated details remain unconfirmed. |
Use current provider documentation to check time-source traceability, security controls and audit scope; do not assume a standard sets the same audit schedule or number of time sources for every provider.
Tips for Safe Time-Stamping
- Pick TSAs that follow the latest NIST guidelines and use a secure timestamp certificate generator.
- Update your time-stamping software regularly.
- Use multiple TSAs for critical documents to increase security.
- Keep an eye on your time-stamped documents and check their validity periodically.
- Train your team on the importance of time-stamp security and proper usage.
Legal Rules for Time-Stamping
Laws About Time-Stamping
Time-stamping laws vary by country. Key laws include:
- US: E-SIGN Act (2000) – Recognizes electronic signatures and records
- EU: Regulation (EU) No 910/2014 on eIDAS, as amended by Regulation (EU) 2024/1183, covers electronic identification and trust services, including electronic timestamps. Read the amendment
Other legal points:
- Follow data protection laws (like GDPR in EU)
- Meet industry rules (e.g., FDA 21 CFR Part 11 for pharma)
- Keep electronic records safe long-term
Using Time-Stamped Content in Court
For time-stamped content to work in court, it needs:
- To be real: Others can check it’s not fake
- To be trusted: From a known, good time-stamp provider
- To be unchanged: Content is the same as when stamped
Courts look at:
- How good the time-stamp provider is
- The math used to make the time-stamp
- Who had the content and when
- What experts say about the time-stamp
Time-Stamping Rules for Different Industries
| Industry | Rule | What It Says |
|---|---|---|
| Finance | EU clock-synchronisation rules | Accuracy requirements vary by system and trading activity. See Commission Delegated Regulation (EU) 2025/1155. |
| Healthcare | Applicable privacy and security requirements | Check the requirements for the specific records and system; do not assume a universal timestamp rule |
| Legal | Federal Rules of Evidence (US) | Sets rules for using electronic records in court |
To follow the rules:
- Know your industry’s rules
- Use good time-stamping that meets or beats the rules
- Check and update how you time-stamp often
- Ask lawyers to make sure you’re following the rules
Time-Stamping and Recordkeeping Risks
A timestamp can support a recordkeeping trail, but it does not by itself establish legal or regulatory compliance. Check the recordkeeping and clock-synchronization rules that apply to the activity and jurisdiction.
Tips for Legal Time-Stamping
- Use trusted time-stamp providers
- Keep your time-stamping tech up-to-date
- Train staff on time-stamping rules
- Have a plan to check time-stamps regularly
- Work with legal experts to stay on top of new laws
New Time-Stamping Methods
Blockchain for Time-Stamping
Blockchain in content distribution and copyright management offers a new way to time-stamp digital content. It uses a shared database to record when something happened, making it hard to change or fake.
Key features of blockchain time-stamping:
- No central authority needed
- Records can’t be changed once made
- Anyone can check the timestamps
ScoreDetect offers blockchain timestamping. A timestamp can help show when a matching file hash was recorded; it does not prove who created the file.
Distributed Ledgers in Time-Stamping
Distributed ledger technology (DLT) builds on blockchain ideas. It spreads timestamp data across many computers, making it safer and able to handle more information.
DLT time-stamping helps with:
- Handling lots of timestamps at once
- Keeping data safe by storing it in many places
- Processing timestamps faster
In supply chains, DLT time-stamping tracks products from start to finish. This helps stop fake goods and makes the whole process clearer.
Post-Quantum Cryptography and Time-Stamping
NIST’s first principal post-quantum cryptography standards, released in August 2024, specify key-establishment and digital-signature schemes. They address cryptographic algorithms, not clock accuracy; organizations adopting them need to plan updates to affected systems. See NIST’s post-quantum cryptography standards overview.
Real-World Use of New Time-Stamping
| Company | What They Did | Result |
|---|---|---|
| ScoreDetect | Offers blockchain timestamping | A timestamp can help show when a matching file hash was recorded; it does not prove who created the file |
| IBM | Tested DLT in supply chains | Tracked goods better, reduced fake products |
| Researched quantum-safe algorithms | Working on future-proof time-stamping methods |
Blockchain Time-Stamping in Action
A supply-chain team can timestamp records at handoffs to create a chronological record. A timestamp can help show when a record was submitted, but it does not by itself prove that the recorded event occurred or that the underlying information is correct.
Tips for Using New Time-Stamping Methods
- Look into blockchain-based services for important documents
- Consider DLT for business processes that need lots of timestamps
- Stay informed about quantum-safe methods for long-term security
- Test new time-stamping tech on a small scale before full adoption
- Train your team on how to use and check new time-stamps
Problems with Time-Stamping
Clock Sync Problems
Keeping clocks in sync is a big challenge for time-stamping:
- Network delays can cause time differences
- Computer clocks drift over time
- Time zones and daylight saving time add complexity
Network Time Protocol (NTP) performance depends on the time source, implementation and network conditions:
| NTP Accuracy | Typical Range |
|---|---|
| Standard | Varies with the time source, implementation and network conditions |
For better accuracy, some use Precision Time Protocol (PTP).
Issues with Large-Scale Time-Stamping
As more content needs time-stamps, new problems come up:
- Time Stamping Authorities (TSAs) can get overloaded
- Storing all time-stamps takes up a lot of space
- Checking many time-stamps takes a long time
Some companies are looking at blockchain and other new ways to handle more time-stamps.
Making Different Time-Stamping Systems Work Together
Getting different time-stamping systems to work together is hard:
- Systems may use different rules
- It’s tough to trust time-stamps from other systems
- Time-stamps may look different across systems
To fix this, people are working on common rules. Many now use RFC 3161 Time-Stamp Protocol (TSP) to make systems work better together.
Clock Synchronization and Record Traceability
Clock errors can affect event ordering and the traceability of trading records. Under applicable EU clock-synchronisation rules, covered firms must be able to demonstrate traceability to Coordinated Universal Time (UTC). Practical controls include monitoring clock offsets, documenting time-source traceability and investigating unexpected drift. See Commission Delegated Regulation (EU) 2025/1155.
| Problem | Impact |
|---|---|
| Wrong timestamps | Can affect event ordering and the traceability of records |
| Regulatory fines | Depend on the applicable rules and the facts of the case |
| System downtime | Duration depends on the incident and recovery process |
What’s Next for Time-Stamping
eIDAS Rules for Qualified Electronic Timestamps
Regulation (EU) 2024/1183 amended the eIDAS framework. It recognizes qualified electronic timestamps provided in one Member State in all other Member States, and provides a presumption of compliance when binding date and time to data and time-source accuracy meet applicable standards and procedures. Read the regulation.
The amendment provides for:
| Change | What It Means |
|---|---|
| Stricter TSA Rules | The amendment provides a presumption when date/time binding and time-source accuracy meet referenced standards and procedures |
| EU-wide Acceptance | Qualified electronic timestamps provided in one Member State are recognized in all other Member States |
| Blockchain Guidelines | The amendment distinguishes electronic ledgers from electronic timestamps |
The amendment distinguishes qualified electronic timestamps from electronic ledgers; it does not require timestamp providers to use blockchain.
AI and Machine Learning in Time-Stamping
Automated analysis can help flag unusual timestamp data, but it does not replace cryptographic validation. RFC 3161 describes the timestamp token and verification checks; see the RFC 3161 specification.
How Quantum Computing Might Change Time-Stamping
Quantum computing could both help and hurt time-stamping. It might break current time-stamping math, but it could also make time measurements super accurate.
NIST released its first principal post-quantum cryptography standards in August 2024. The standards cover key establishment and digital signatures; they do not establish clock-synchronization accuracy. See NIST’s post-quantum cryptography standards overview.
New quantum time-stamping tech:
| Tech | What It Could Do |
|---|---|
| Quantum Key Sharing | ML-KEM is a post-quantum key-establishment standard, not a quantum key-distribution or timestamping method |
| Quantum Clock Sync | NIST’s post-quantum cryptography standards do not specify clock-synchronization accuracy |
| Post-Quantum Math | ML-DSA and SLH-DSA are digital-signature standards |
As these new tools get better, we’ll see time-stamping that’s much safer and more accurate. This will change how we protect and check digital content.
Wrap-Up
A verified timestamp can help support that matching data existed by a given time, but it does not establish authorship or prove that content is authentic. Time-stamping can form one part of a content protection strategy; see our guide to content protection.
Key Takeaways
| Aspect | Importance |
|---|---|
| Cryptographic basics | Foundation for secure time-stamping |
| Standards compliance | Ensures reliability and interoperability |
| Security measures | Protects against tampering and fraud |
| Implementation best practices | Maintains long-term validity |
| Emerging technologies | Shapes the future of time-stamping |
Future Developments
1. eIDAS amendment (Regulation (EU) 2024/1183)
- Qualified electronic timestamps provided in one Member State are recognized in all other Member States
- Provides a compliance presumption when date/time binding and time-source accuracy meet referenced standards and procedures. Read the regulation
- Guidelines for blockchain timestamps in creative industries
2. Automated anomaly checks
Automated checks may help flag unusual timestamp data, but cryptographic token verification and accurate, traceable time sources remain necessary.
3. Post-quantum cryptography
NIST released its first principal post-quantum cryptography standards in August 2024. The standards cover key establishment and digital signatures; see NIST’s standards overview.
| Technology | Potential Impact |
|---|---|
| Quantum Key Sharing | NIST’s ML-KEM is a post-quantum key-establishment standard; it does not make timestamp transmission unhackable |
| Quantum Clock Sync | NIST’s standards do not establish clock synchronization or nanosecond accuracy |
| Post-Quantum Algorithms | ML-DSA and SLH-DSA are standards for digital signatures |
Action Steps
- Update time-stamping systems regularly
- Stay informed about new standards and regulations
- Explore AI applications for timestamp verification
- Consider quantum computing’s impact on current methods
Extra Info: Tools and Resources
Free Time-Stamping Software
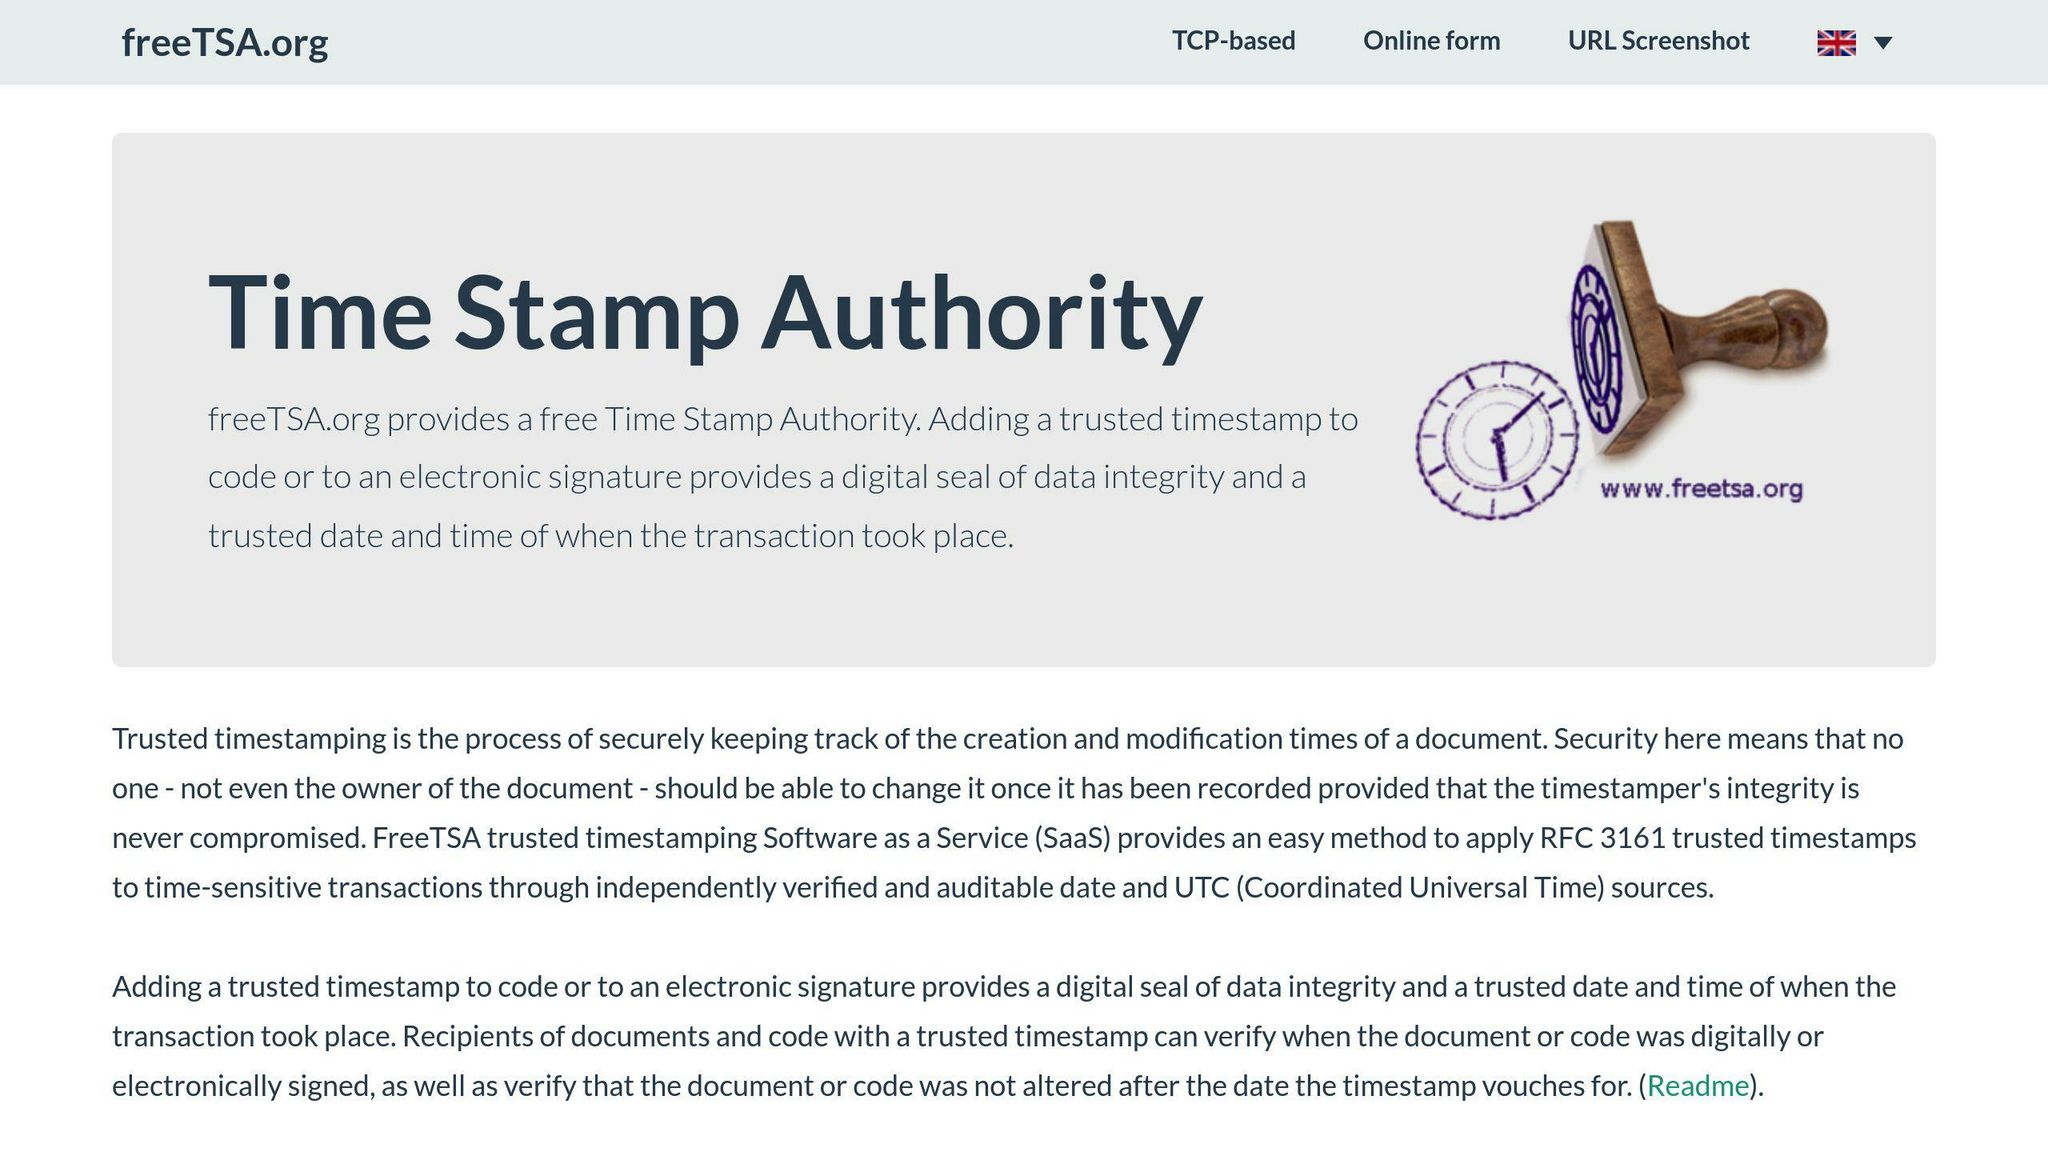
FreeTSA offers a free service for applying RFC 3161 trusted timestamps to digital content. Key features include:
- Timestamps multiple files by creating an aggregate file with fingerprints
- Works on desktop and mobile devices (Android/iOS)
- No software installation needed for mobile use
Paid Time-Stamping Services
For users with specific needs or large-scale requirements, FreeTSA provides custom solutions. Contact them directly for:
- Tailored time-stamping services
- Additional features like free OCSP, CRL, and NTP
Practical Time-Stamping Tools
FreeTSA offers several tools to help users implement time-stamping:
| Tool | Purpose |
|---|---|
| Online Signature | Timestamp photos/videos directly from device cameras |
| Command-line tools | For advanced users and automation |
| PDF signing documentation | Guide for adding timestamps to PDF documents |
Where to Learn More
To explore FreeTSA’s services:
- Visit freetsa.org
- Access via Tor: 4bvu5sj5xok272x6cjx4uurvsbsdigaxfmzqy3n3eita272vfopforqd.onion
Tips for Using FreeTSA
- For multiple files:
- Create a text file with SHA-512 hashes of your files
- Or pack files into a zip/rar/img/tar and timestamp it
- Use the "Online Signature" feature to timestamp photos or videos on-the-go
- Explore FreeTSA’s free services for time synchronization and encrypted name resolution
Technical Details
FreeTSA supports:
- Both IPv4 and IPv6 addresses
- Various time-related services (NTP, DNSCRYPT, DNS over TLS)
This combination of features makes FreeTSA a versatile tool for users needing reliable time-stamping services across different platforms and use cases.